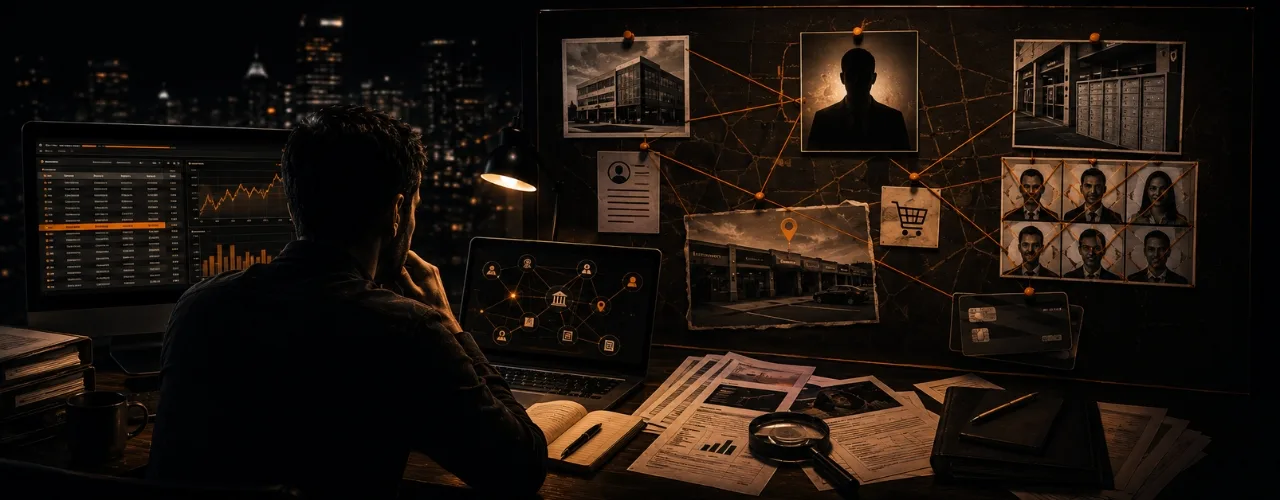
A finance team flagged a string of mid-sized payments to a new software maintenance contractor. Nothing alarming, just tidy monthly invoices that slipped neatly into the budget. It took OSINT investigations to show what the ledger could not.
But when an analyst ran a quick OSINT investigation, the picture changed immediately. The company’s website was a month old. Its team photos were stock images.
The founder’s LinkedIn profile showed three jobs all starting on the same date. Its address was a mailbox in a strip mall. Internally, the transactions looked normal. Externally, the story fell apart in minutes.
That’s open source intelligence in practice. Not hacking. Not surveillance. Just knowing where to look in what’s already publicly available, and knowing how to connect what you find.
What OSINT Investigations Actually Are
Open source intelligence is the practice of turning publicly accessible data into actionable intelligence. Effective use of data can significantly increase the impact of investigations. That data comes from corporate registries, surface, deep and dark web sources, social media, adverse news providers, and more. The distinction between data and intelligence is what matters. A list of social media posts is data. Knowing that those posts, cross-referenced against a corporate filing and a vessel tracking record, place a specific person at a specific location at a specific time is intelligence.
With more than 402.74 million terabytes of data created daily as of 2026, the challenge isn’t access to information. It’s knowing which sources are relevant and how to verify what you find. It’s also knowing how to assemble individual data points into something that means something. That’s what OSINT investigations deliver. However, most people outside the industry don’t fully understand what the methodology actually looks like.
A 2025 report found that 71% of anti-financial crime professionals expected financial crime risks to increase. Only 23% believed their organization’s compliance program was very effective. Modern fraud networks leave signals in digital environments long before funds move through financial systems. That is exactly where online investigation using OSINT methodology intercepts them.
Where OSINT Investigations Find the Digital Trail
OSINT investigations draw on a wider range of sources than most people realize.
Social media platforms are one layer. They offer more than public profiles, including behavioral patterns, metadata embedded in posts and images, account activity timing, and cross-platform username reuse that connects apparently separate identities. For example, a reused handle, an email address format, or a distinctive writing style can link an anonymous account to a real person across multiple platforms.
Corporate registries and public filings are another. Shared registered addresses, overlapping directors, and reused formation agents are strong signals. So are circular ownership structures visible in public business registers. Together, they are among the most reliable indicators of shell company networks and organized crime infiltration of legal markets. OSINT from public business registers works as a proxy for identifying local network structures within criminal organizations. It works even when traditional closed-source data is unavailable.
Court records, regulatory databases, sanctions lists, vessel tracking systems, satellite imagery, dark web forums, and leaked document repositories round out the picture. Each source contributes a different layer of the digital footprint investigation. However, the intelligence value is usually in how those layers intersect, not in any single source alone.
How OSINT Investigations Map Criminal Networks
The most significant feature of open source intelligence in complex investigations isn’t the individual findings. It’s the network they reveal.
Criminal networks rely on connections to function between people, between entities, between infrastructure. Moreover, identifying one individual in a network often surfaces a web of accomplices. Social network analysis visualizes relationships between individuals, organizations, and locations. It identifies the gatekeepers whose removal would most disrupt an operation. Deanonymization also helps: cross-referencing phone numbers, email addresses, and usernames across platforms converts an anonymous digital presence into a real identity.
How OSINT Investigations Expose Infiltration and Trafficking
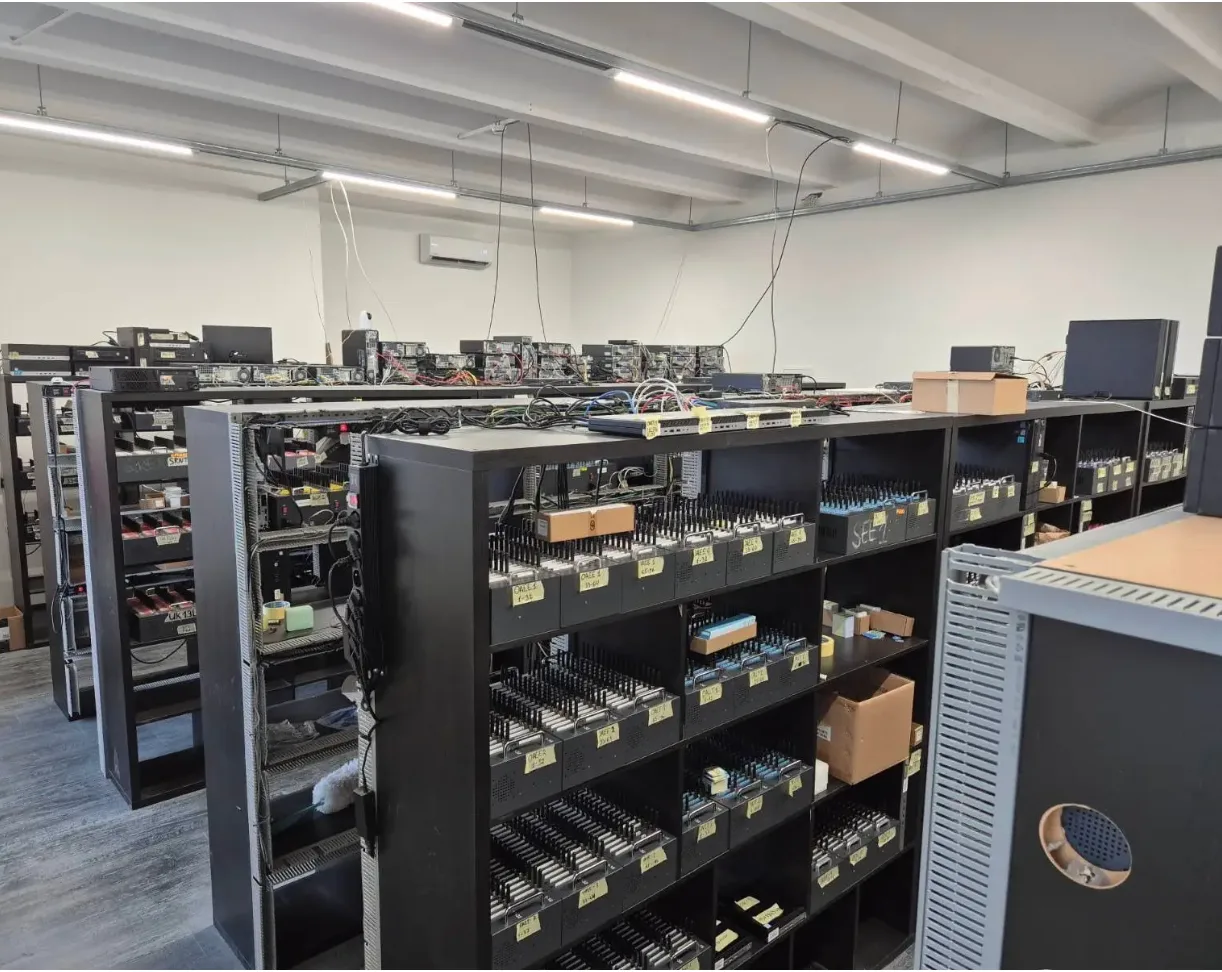
OSINT also exposes how organized crime infiltrates legitimate corporate structures. A company that looks clean in a registry search may share directors, addresses, or formation agents with entities that appear in sanctions databases or adverse media. Fraud networks now operate across broad networks of web platforms, identity systems, and financial networks simultaneously. Digital footprint investigation across those platforms is often what reveals how they’re connected.
Human trafficking networks use the same infrastructure. Specifically, traffickers create fake job advertisements online to lure victims into forced labor, sexual exploitation, or scam compound operations. OSINT enables investigators to detect recruitment sites, uncover false postings, and map smuggling routes. It also helps them expose criminal networks and trace illicit financial flows, often before any financial transaction has occurred.
OSINT Investigations in Financial Crime
Digital networks that function outside the traditional financial system increasingly structure and organize financial crime. Modern financial crime controls aim to detect suspicious transactions. However, investigators regularly encounter cases where the network behind the fraudulent transactions was active online before any suspicious financial activity became visible.
Online investigation using OSINT bridges that gap. In sanctions evasion cases, combining sanctions lists with vessel tracking data identifies suspicious shipping routes. These include vessels engaging in flag switching, disabling AIS transponders, or routing through intermediary ports to obscure the true origin or destination of cargo. In corporate fraud cases, the software maintenance contractor scenario at the opening of this blog is one version of a pattern that repeats across industries. A vendor looks legitimate in internal records but collapses under a basic OSINT investigation of its external footprint.
Fraud now accounts for 45% of all crime in England and Wales. Organizations recorded over 444,000 fraud cases in 2025, the highest annual figure reported to the UK’s National Fraud Database. As a result, professional investigation services that combine financial intelligence with OSINT methodology increasingly identify those networks before the damage becomes irreversible.
From Lead to Admissible Evidence
OSINT investigations excel at generating leads. Courts require something more rigorous.
Converting an OSINT finding into admissible evidence requires timestamped records of when and how you collected the information, documented methodology, and authentication protocols proving the content stayed unaltered between collection and presentation. The operational security dimension matters equally. If a subject recognizes investigative activity in their digital environment, they may delete accounts, alter behavior, or move assets. They can do so before the investigation finishes. Professional investigation services conducting OSINT investigations specifically train their investigators to avoid that.
There’s also a fragmentation problem. Relevant data in a complex digital footprint investigation typically spreads across corporate registries, social media platforms, leaked document repositories, and dark web forums. Those systems don’t communicate with each other. Assembling a coherent picture from those fragments is most of the actual work. It’s also where experience and methodology make the difference between a lead and a case.
The Tools Behind the Methodology
None of this works without the right infrastructure. A handful of platforms and tools show up repeatedly in professional OSINT practice, each suited to a different layer of the investigation.
For corporate structure, OpenCorporates is a starting point for many investigators. Registering for its free “Permitted User” tier (open to journalists, NGOs, and academics) unlocks the fullest public dataset and its advanced filtering tools, useful for tracing shared directors or registered addresses across jurisdictions.
For cross-referencing leaked and public records at scale, OCCRP’s Aleph aggregates and visualizes data from millions of documents, including company registries and major leak datasets like the Panama and Paradise Papers. It’s free for journalists and built specifically for the kind of document-fragment assembly described above.
Once you gather the individual data points, you need to map them. Link-analysis software like Maltego is built for visualizing complex networks of entities, officers, and addresses; lighter-weight mind-mapping tools such as XMind or draw.io can serve the same purpose for smaller cases.
And because so much of this work is jurisdiction-specific, experienced investigators keep a working list of high-value national registries, UK Companies House being one of the more heavily used examples, since registry quality and disclosure requirements vary considerably from one country to the next.
The Pattern Was Always There
Criminal networks, fraudulent companies, and individuals hiding assets all rely on the same assumption: that the connections between them are invisible. OSINT investigations exist because that assumption is consistently wrong.
The software maintenance contractor’s fake website, the burglary ring’s iCloud selfie, the sanctions evader’s vessel routing, in each case, the trail was in public view. It simply needed someone trained to follow it, and professional investigation services with the methodology to do it in a way that holds up.
If your matter involves a counterparty, individual, or network that warrants a digital footprint investigation, the first conversation is confidential. You can also learn more about our OSINT and evidence analysis and enhanced due diligence services.
FAQs
What is an OSINT investigation?
An OSINT investigation is the structured collection and analysis of publicly available information from social media, corporate registries, court records, vessel tracking systems, and other open sources to generate actionable intelligence. Unlike hacking or surveillance, open source intelligence works entirely within what’s already publicly accessible. That makes it both legally defensible and often the fastest route to understanding who you’re actually dealing with.
What sources does an OSINT investigation draw on?
OSINT investigations draw on social media platforms, corporate registry and public filing databases, court records, regulatory and sanctions databases, dark web forums, vessel tracking and satellite imagery, leaked document repositories, and adverse news archives. However, the intelligence value typically lies in how these sources intersect, not in any single source alone.
Can OSINT findings be used as evidence in court?
Yes, provided they’ve been collected and documented to evidentiary standards. Specifically, this requires timestamped records, documented methodology, and authentication protocols demonstrating the content wasn’t altered between collection and presentation. Professional investigation services conducting OSINT investigations build these requirements into their methodology from the start.
How does OSINT differ from hacking or illegal surveillance?
Open source intelligence operates entirely within publicly available information, no unauthorized access, no interception of private communications. In short, the legal and ethical boundary is between what’s publicly accessible and what requires authorization to access. OSINT investigations stay entirely on the public side of that line.
How does CAT Investigators use OSINT in its work?
CAT Investigators uses open source intelligence as a core component of due diligence, criminal investigations, financial crime work, and corporate investigations. Our online investigation capability spans social media analysis, corporate structure mapping, sanctions screening, digital footprint investigation, and network analysis across multiple jurisdictions. As part of our professional investigation services, every finding is documented to the standard required for legal proceedings. Reach out for a confidential consultation.
Sources
- How OSINT Supports Financial Crime Investigations: Fraud, Sanctions Evasion, and Money Laundering
- Why OSINT Is Becoming Essential for Financial Crime Investigations in 2026
- Following the Money Isn’t Enough Anymore: OSINT and Financial Intelligence
- OSINT and Financial Crime: Seeing the Story Behind the Numbers
- The Best OSINT Investigation Tools for Fighting Financial Crime: Kroll 2025 Report
- Using Open-Source Intelligence to Investigate Human Trafficking and Migrant Smuggling